


Overview
Controlling access to files and directories sits at the core of Unix-like operating system security. This practical walkthrough breaks down how the chmod utility works, contrasting octal modes (such as 755 and 644) with symbolic notation (rwx). Through hands-on shell demonstrations, you will gain a solid mental model of permission masks and how to enforce least privilege across your systems.
1. Inspecting Permission Bits via ls -l
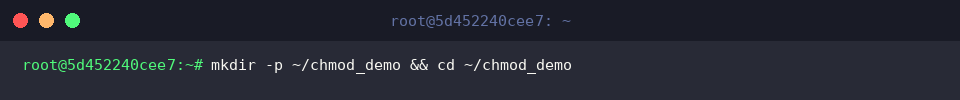
To keep our experimentation isolated from the rest of the filesystem, spin up a dedicated playground directory and switch into it:
mkdir -p ~/chmod_demo && cd ~/chmod_demo
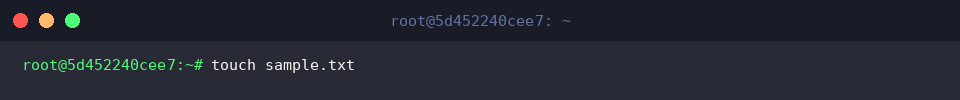
Next, generate a blank test file so we have a target for our permission inspections:
touch sample.txt
Now, inspect the newly generated item’s metadata and baseline permissions by running:
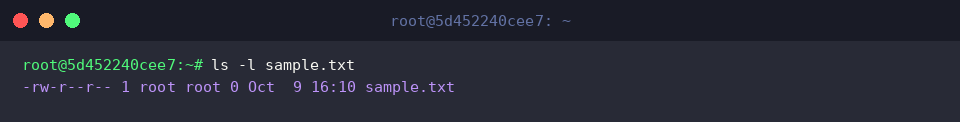
ls -l sample.txt
The initial 10-character string (-rw-r--r--) breaks down the entry’s nature and capabilities: the leading dash identifies a standard regular file, followed by triad segments that grant read/write rights to the file owner, read-only privileges to members of the owning group, and read-only access to all other accounts on the system.
⚙️ [Essential Command-Line Flags]
-l : Generates an itemized long-listing format including file mode, link count, owner, group, byte size, and modification timestamp.-a : Reveals every directory member, bypassing the exclusion filter on dotfiles (hidden files beginning with .).-h : Prints file sizes in convenient binary scale suffixes (such as K, M, or G) when coupled with the -l flag.-d : Prevents descent into directories, outputting metadata for the container itself instead of listing its contents.-R : Traverses directory structures downward in a recursive manner, cataloging subtrees entirely.
2. Managing Access Rights Using Numeric Octal Modes (644 vs. 755)
Ensure your active shell prompt is situated inside the experiment directory:
cd ~/chmod_demo
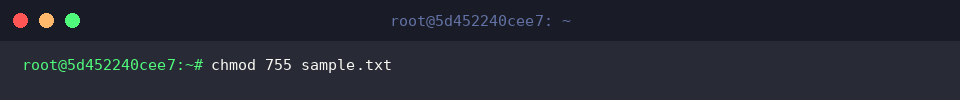
Octal syntax calculates bitmasks by summing weight values: read (r = 4), write (w = 2), and execute (x = 1). To grant the owner full rights (4+2+1 = 7) while limiting group members and others to reading and executing (4+1 = 5), execute:
chmod 755 sample.txt
Verify how the permission triplets evolved with:
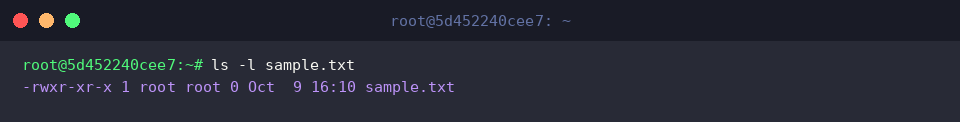
ls -l sample.txt
The bitfield now reads -rwxr-xr-x. The owner triad displays full rwx capabilities, while the group and world triads show r-x, confirming the execution bit is enabled across all three scopes.
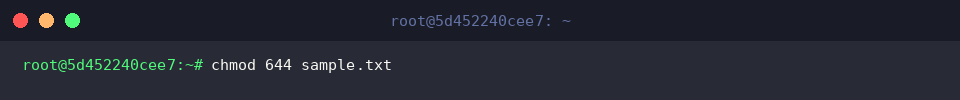
Most plain documents and configuration files should not carry executable privileges. To revert this target to standard document permissions—read/write for the owner (6) and read-only for everyone else (4):
chmod 644 sample.txt
Re-examine the file properties:
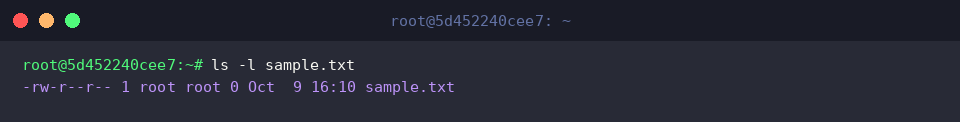
ls -l sample.txt
The mode string reflects -rw-r--r--, stripping execution privileges entirely and keeping write permissions restricted solely to the file’s owner.
3. Granular Bit Manipulation via Symbolic Notation
Return to the demo directory if you have shifted locations:
cd ~/chmod_demo
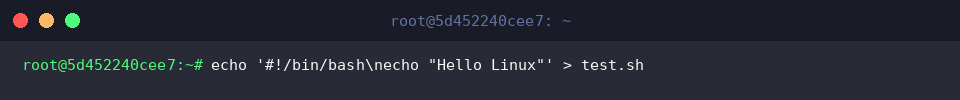
Let’s craft a quick shell script to demonstrate dynamic flag toggling:
echo '#!/bin/bash\necho "Hello Linux"' > test.sh
Rather than recalculating three octal digits, symbolic mode lets you target specific bits directly. To mark this script executable for everyone (user, group, and others simultaneously), use:
chmod +x test.sh
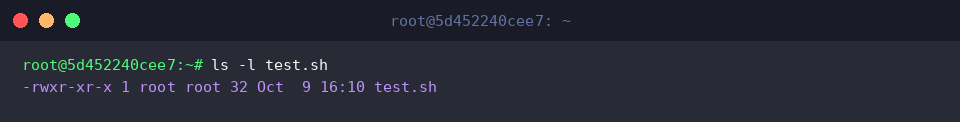
Check the resulting bitmask:
ls -l test.sh
The listing outputs -rwxr-xr-x, indicating that execution privileges (x) were seamlessly enabled across the board without overriding existing read or write settings.
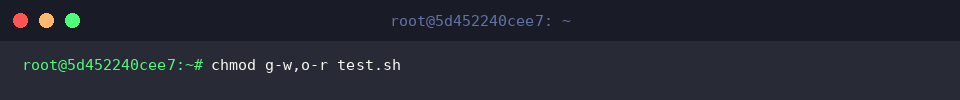
Symbolic commands can also combine multiple modifications in a single invocation using commas. To revoke write access from the group while stripping read rights from others:
chmod g-w,o-r test.sh
Confirm the altered permission mask:
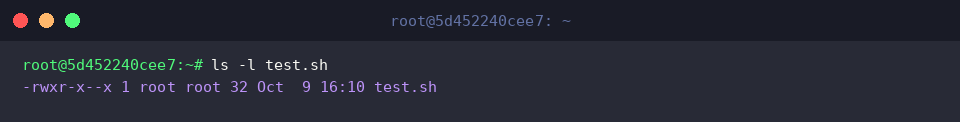
ls -l test.sh
The field shifts to -rwxr-x--x, showing that group write capability remains disabled while foreign accounts retain only raw execute rights without the ability to inspect script contents.
4. Bulk Permission Updates Across Directory Trees (-R)
In server administration, you will frequently need to align security profiles across entire software stacks. Let’s build a nested directory layout simulating an application deployment:
mkdir -p ~/chmod_demo/project/logs
Populate the project tree with dummy artifacts:
touch ~/chmod_demo/project/app.py ~/chmod_demo/project/logs/app.log
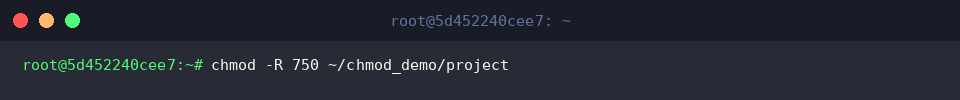
To recursively enforce mode 750 across the container and every nested item beneath it, append the -R flag:
chmod -R 750 ~/chmod_demo/project
This applies full access (7) to the owner, read and traversal capabilities (5) to the group, and locks out untrusted external users (0) from the entire tree hierarchy.
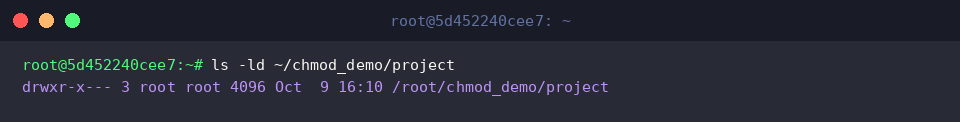
Inspect the top-level directory itself using -d to prevent ls from expanding internal files:
ls -ld ~/chmod_demo/project
The output confirms drwxr-x---, validating that the directory root adopted owner full control, group read/execute, and zero access for the world.
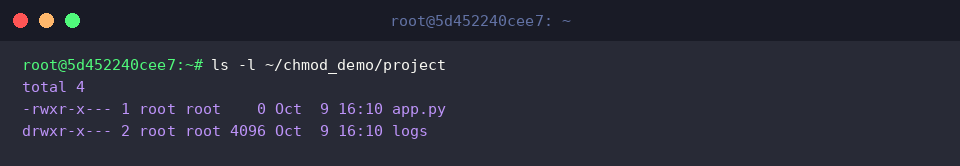
Finally, examine the tree contents to ensure child nodes inherited the update:
ls -l ~/chmod_demo/project
Both app.py and the nested logs/ directory reflect -rwxr-x--- and drwxr-x--- respectively, confirming that the recursive operation traversed down the entire branch as intended.
Understanding the distinction between octal and symbolic modes empowers you to harden Linux servers efficiently while avoiding common misconfigurations. Applying the principle of least privilege ensures your sensitive data and executable assets stay safe from unauthorized modification.