


Overview
Built around the cryptographic BLAKE2b hashing algorithm, b2sum provides Linux administrators with an exceptionally fast utility for confirming file integrity. While classic hashing utilities like md5sum suffer from known vulnerabilities and sha256sum can become sluggish on massive datasets, b2sum combines cryptanalytic resilience with unmatched processing throughput. In this tutorial, we will explore practical workflows for producing hash digests and validating files against tampering in an Ubuntu environment.
Basic b2sum Usage: Generating File Checksums
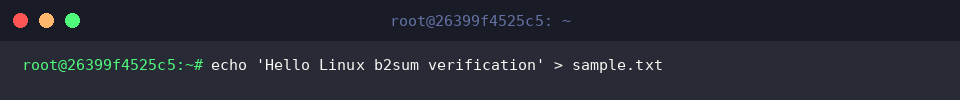
To kick off our hands-on walkthrough, start by assembling a simple test file using echo 'Hello Linux b2sum verification' > sample.txt.
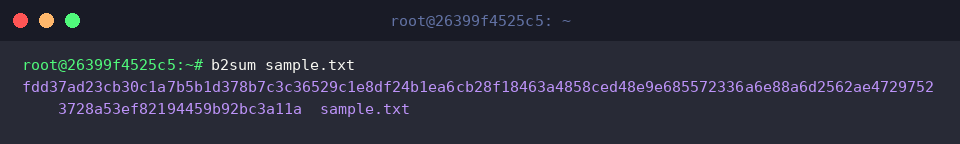
By default, executing b2sum computes a 512-bit cryptographic BLAKE2b digest for target files, emitting the raw hex string alongside the filename to confirm data consistency.
⚙️ [Essential Command-Line Flags]
-c : Reads checksum manifests to validate matching files on disk.-l : Customizes digest bit width (up to 512 bits, must be a multiple of 8).--tag : Formats output using BSD-style syntax.--quiet : Suppresses passing (OK) status lines, alerting only when mismatches occur.--status : Operates silently without terminal output, signaling verification outcomes strictly through process exit codes.
Storing Checksums and Automating Integrity Verification (-c Flag)
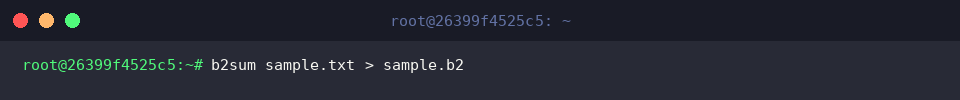
Rather than inspecting strings manually, capture the calculated fingerprint into a manifest file via b2sum sample.txt > sample.b2.
Standard shell redirection (>) routes stdout directly into the target file, generating your baseline signature silently without console noise.
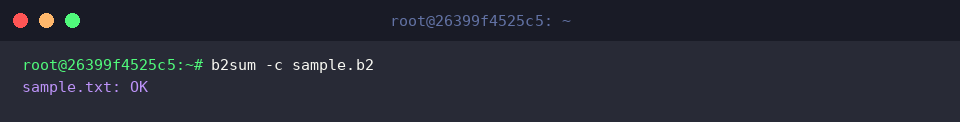
When it is time to audit your assets against unauthorized alterations or corruption, run b2sum -c sample.b2.
A clean report displaying sample.txt: OK confirms that the file has remained bit-for-bit identical to its original state.
Adjusting Digest Bit Length with the -l Option
To examine variable digest lengths, provision another artifact by typing echo 'Digest length test file' > length_test.txt.
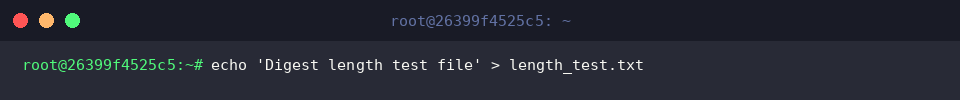
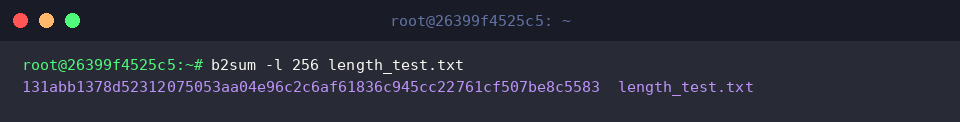
If system specifications or storage constraints call for a shorter hash, invoke b2sum -l 256 length_test.txt.
In place of the standard 512-bit representation (128 hex characters), the output renders a compact 256-bit fingerprint spanning precisely 64 hexadecimal characters.
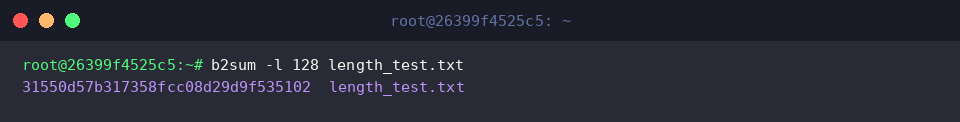
You can scale the digest down further by passing -l 128 to b2sum -l 128 length_test.txt.
This yields a 32-character hexadecimal digest matching 128 bits, proving how dynamically BLAKE2b adapts across bandwidth-sensitive or legacy environments.
Batch Processing and Pipeline Streaming via Standard Input
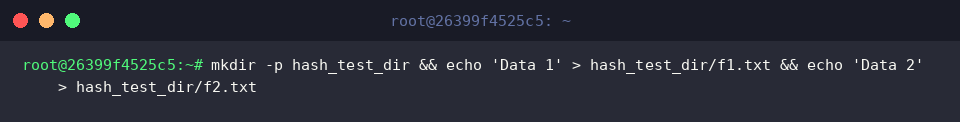
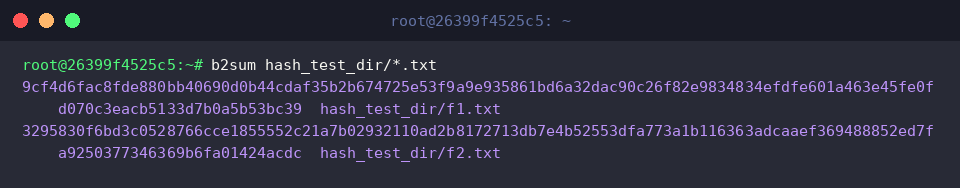
To demonstrate batch calculation across directories, set up a test hierarchy and seed it with items: mkdir -p hash_test_dir && echo 'Data 1' > hash_test_dir/f1.txt && echo 'Data 2' > hash_test_dir/f2.txt.
Wildcard expansion (*) simplifies bulk checks across entire directory trees; execute b2sum hash_test_dir/*.txt.
The utility processes each matching entry sequentially, emitting individual BLAKE2b hashes alongside relative paths for immediate multi-file inspection.
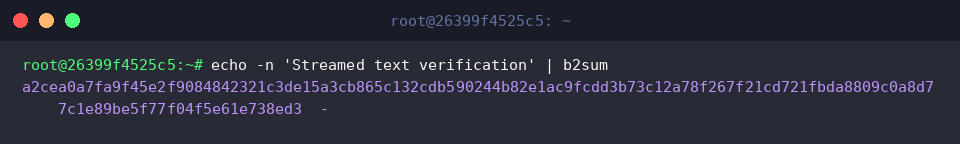
Disk persistence is not mandatory—you can also pipe arbitrary memory or network streams straight into b2sum using echo -n 'Streamed text verification' | b2sum.
The standard hyphen (-) designates stdin processing, showing how seamlessly BLAKE2b embeds into complex continuous delivery pipelines and real-time telemetry filters.
You now have a solid operational command of b2sum for hardening file verification routines on Linux systems.
Whenever data integrity and raw cryptographic speed are paramount, leverage BLAKE2 to ensure resilient, high-speed data protection.