


Overview
Standard POSIX permissions often fall short when mitigating catastrophic mistakes by privileged users or root compromises. Linux extended file attributes bridge this security gap via the chattr utility, enabling administrators to lock down critical data beyond the reach of standard superuser rights. In this hands-on tutorial, we explore how to inspect extended attributes using lsattr, deploy immutable flags (+i) to thwart tampering or accidental deletion, and enforce append-only policies (+a) tailored for audit trails and system logs.
Inspecting Extended Attributes with lsattr
To establish an isolated sandbox for testing file attributes, initialize a dedicated working directory and switch into it by running mkdir -p ~/chattr_demo && cd ~/chattr_demo.
Next, generate a dummy configuration file for experimentation using touch secure_config.conf.
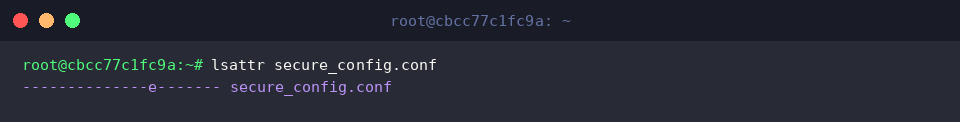
The lsattr utility reads and displays the extended attribute flags associated with files on Linux second-extended file systems (such as ext4).
In the baseline output, the e indicator simply denotes that the filesystem allocates blocks using extents—a standard performance mechanism across modern ext4 partitions.
⚙️ [Essential Command Flags]
-a : Lists extended attributes for every item in the target directory, including hidden dotfiles.-d : Queries the directory itself as a file entry rather than displaying its nested contents.-R : Traverses the filesystem hierarchy recursively to inspect subdirectories and files.-v : Surfaces the internal file version or generation number metadata.
Locking Down Files Against Root Deletion with the +i Flag
To render a file completely unmodifiable, grant it the immutable flag by executing sudo chattr +i ~/chattr_demo/secure_config.conf.
Once marked with +i, the kernel blocks any modification, truncation, deletion, or renaming operations—imposing a hard restriction that even the root user cannot bypass.
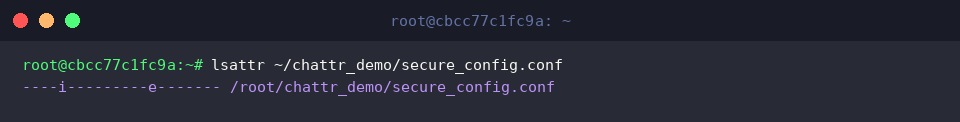
Verify that the attribute took effect by running lsattr ~/chattr_demo/secure_config.conf.
The newly surfaced i flag confirms that write and unlink privileges are now locked down on the target inode.
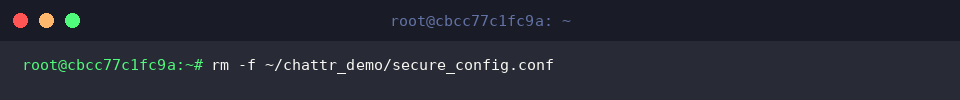
Test the resilience of this policy by attempting an unconditional forced deletion via rm -f ~/chattr_demo/secure_config.conf.
Despite the -f override switch, the filesystem rebuffs the deletion request, leaving the protected asset completely intact.
Removing Immutable Locks for Maintenance (-i Option)
When configuration updates or routine cleanups are required, strip the lockdown flag by executing sudo chattr -i ~/chattr_demo/secure_config.conf.
Invoking -i releases the immutable restriction, returning the target to conventional POSIX permission handling so legitimate modifications can proceed.
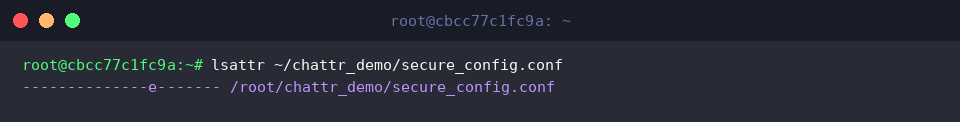
Run lsattr ~/chattr_demo/secure_config.conf to validate that the attribute modification was accepted.
As observed, the i token has vanished from the attribute string, confirming that write protection has been deactivated.
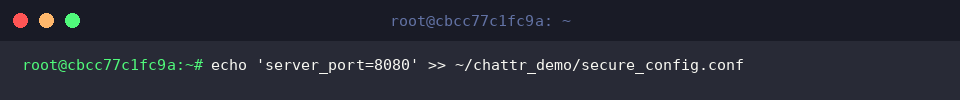
Confirm that write capability is fully restored by appending a sample setting via echo 'server_port=8080' >> ~/chattr_demo/secure_config.conf.
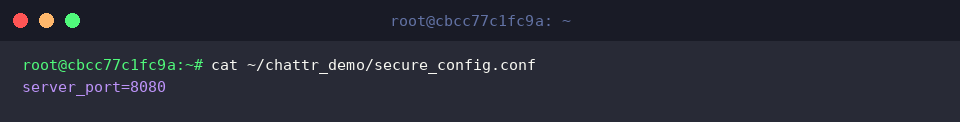
Inspect the file contents by executing cat ~/chattr_demo/secure_config.conf.
The appended configuration string prints cleanly to the terminal, confirming that standard write access is operational once more.
Tamper-Proofing System Logs with Append-Only Mode (+a Option)
To illustrate audit log hardening, generate a fresh log artifact using touch ~/chattr_demo/app_audit.log.
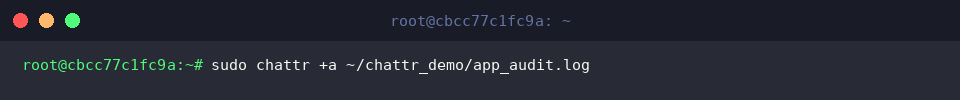
To prevent attackers or compromised processes from wiping or truncating event records while still allowing continuous telemetry ingestion, execute sudo chattr +a ~/chattr_demo/app_audit.log.
The +a attribute mandates append-only behavior: new data streams can be concatenated to the tail of the file, but existing blocks cannot be rewritten or truncated.
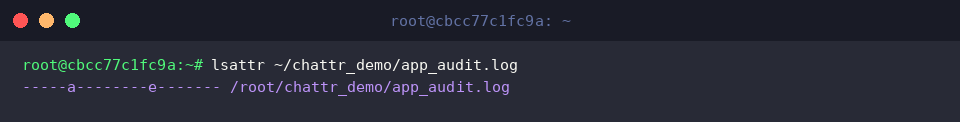
Check the active attribute set by running lsattr ~/chattr_demo/app_audit.log.
The flag display will now exhibit an a attribute, signifying that the file is operating under strict append-only constraints.
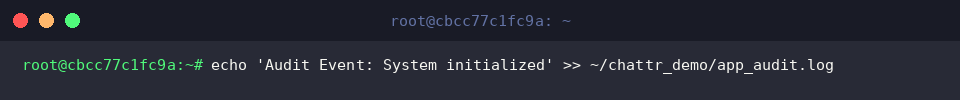
Verify whether logging pipelines can still append data as intended by running echo 'Audit Event: System initialized' >> ~/chattr_demo/app_audit.log.
The write stream completes without friction, proving that the >> redirection operator functions smoothly under the +a policy.
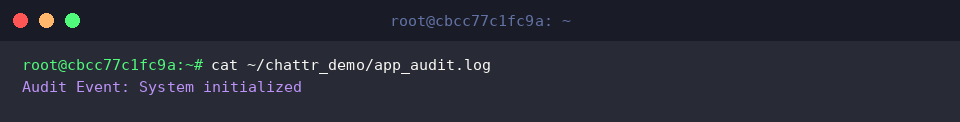
Validate the stored records using cat ~/chattr_demo/app_audit.log.
The newly pushed audit entry appears intact at the end of the file, demonstrating reliable append operations alongside tamper resistance.
Recursive Protection for Directories and Trees (-R Option)
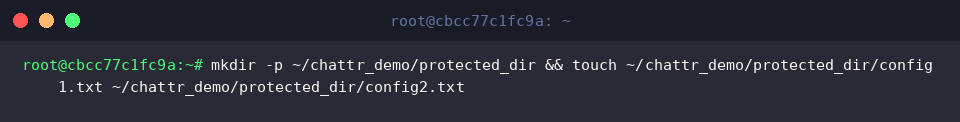
To test directory-level protection strategies, set up a structured folder hierarchy alongside mock files by issuing mkdir -p ~/chattr_demo/protected_dir && touch ~/chattr_demo/protected_dir/config1.txt ~/chattr_demo/protected_dir/config2.txt.
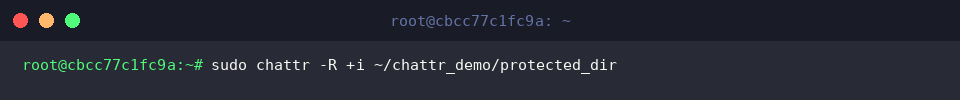
Apply the immutable flag across the entire folder hierarchy in one sweep by executing sudo chattr -R +i ~/chattr_demo/protected_dir.
The -R flag commands chattr to recursively cascade the designated policy to all existing nested subdirectories and files.
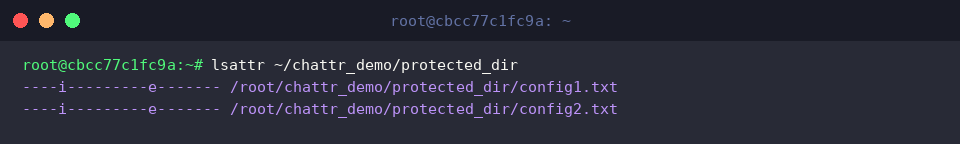
Confirm that the nested files inherited the restriction by running lsattr ~/chattr_demo/protected_dir.
Each individual file inside the folder now carries the i designation, establishing an end-to-end protective shield across the directory structure.
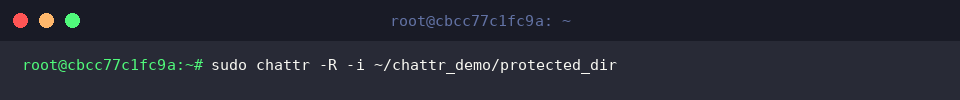
When maintenance tasks necessitate unrestricted access across the hierarchy, revoke the attributes across the board using sudo chattr -R -i ~/chattr_demo/protected_dir.
Pairing -R with -i strips the immutable lock from every nested entity simultaneously, restoring the directory tree to ordinary operational status.
Leveraging extended attributes through chattr and lsattr provides a robust, kernel-enforced line of defense against both malicious tampering and unintentional rm -rf disasters.
By integrating immutable flags onto sensitive credentials and enforcing append-only modes on system journals, administrators can substantially harden their Linux and Ubuntu environments.