


Overview
Manually modifying group passwords across multiple security groups on Linux servers introduces operational friction and human error. Linux administrators can streamline bulk credential provisioning with chgpasswd, an indispensable utility designed for unattended batch password assignments. This practical walkthrough covers standard input ingestion, robust cryptographic cipher selection, and hands-on terminal workflows to modernize your group credential automation.
Environment Preparation: Provisioning System Test Groups
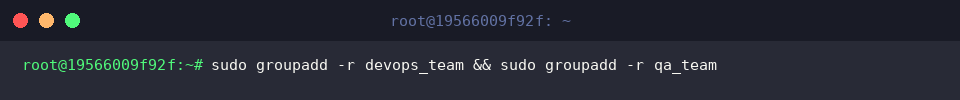
Begin by setting up isolated system groups to benchmark credential modifications safely. Run sudo groupadd -r devops_team && sudo groupadd -r qa_team to provision two test environments.
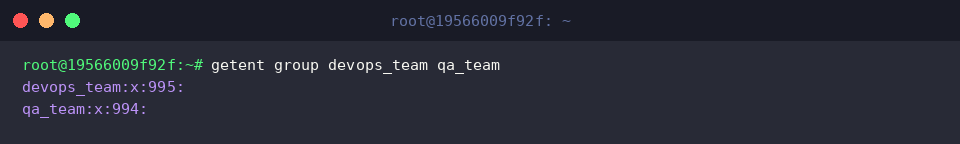
Verify that the Linux identity database successfully registered both group entries by querying getent group devops_team qa_team.
Terminal output confirms the operational status of both entities alongside their assigned system GIDs.
Basic Bulk Credential Provisioning via chgpasswd
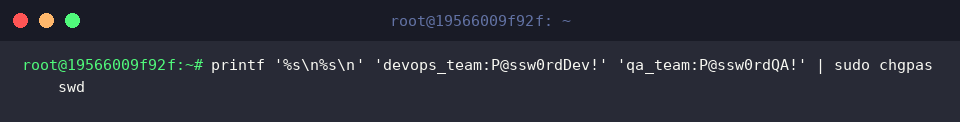
To apply credentials across multiple groups in a single operation, format the payload as groupname:password pairs and feed them into sudo chgpasswd through a standard Unix pipeline.
A silent exit with a zero return code indicates that the operating system has processed and committed all group secrets without error.
Encrypted group secrets reside within /etc/gshadow. Inspect this secure file using sudo grep -E 'devops_team|qa_team' /etc/gshadow to confirm the update took effect.
The command output validates that cryptographic hashes have replaced empty credential slots for both groups.

Hardening Credentials with SHA-512 Encryption (-c)
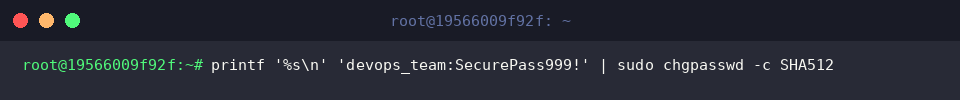
Enforce modern cryptographic security by pairing chgpasswd with the -c SHA512 flag, instructing the subsystem to hash the plaintext payload using SHA-512 before storage: printf '%s\n' 'devops_team:SecurePass999!' | sudo chgpasswd -c SHA512.
The utility completes quietly, signaling that the target group now stores an updated, high-entropy password hash.
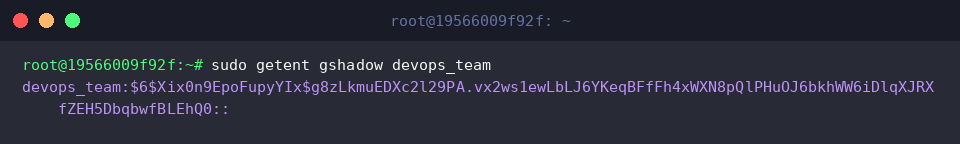
Audit the underlying cryptographic scheme using sudo getent gshadow devops_team.
Notice the password hash begins with the $6$ identifier, confirming that the Linux shadow subsystem successfully persisted a SHA-512 salted digest.
Automated Ingestion via Input Redirection and Teardown
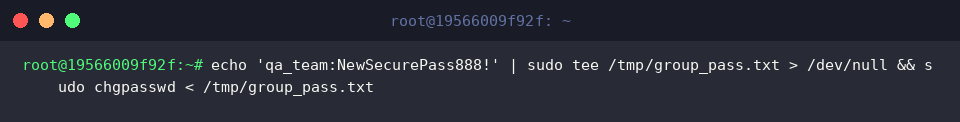
For large infrastructure deployments, store target credentials inside a secure staging file and pipe it directly to the utility using standard shell input redirection (<): echo 'qa_team:NewSecurePass888!' | sudo tee /tmp/group_pass.txt > /dev/null && sudo chgpasswd < /tmp/group_pass.txt.
Clean command completion guarantees that all delimited group definitions within the payload were ingested and synchronized.
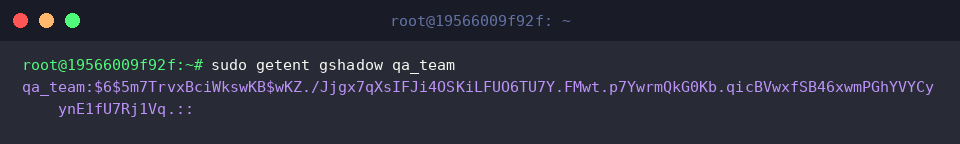
Double-check the newly staged password state on the QA team entity by invoking sudo getent gshadow qa_team.
The entry reflects the updated cryptographic hash corresponding to the redirected file input.
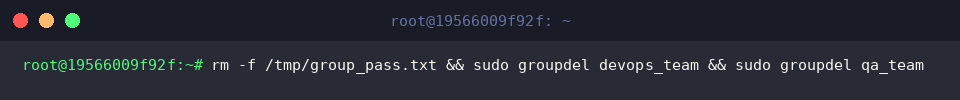
Conclude the lab session by purging staging files and decommissioning the test identities with rm -f /tmp/group_pass.txt && sudo groupdel devops_team && sudo groupdel qa_team.
A quiet return confirms that the temporary credential manifest was eradicated and the test group definitions were fully pruned from the operating system.
Mastering chgpasswd equips systems administrators with a fast, scripting-friendly approach to bulk group authentication management in Ubuntu and Debian-based distributions. Incorporate these input pipelines and hashing standards into your configuration management playbooks to handle fleet-wide security rotations effortlessly.