


Overview
Managing Linux credentials across fleets of accounts often presents friction when relying on interactive tools like passwd. Enter chpasswd, a specialized utility engineered to update authentication secrets non-interactively via standard input. System administrators and DevOps engineers frequently turn to chpasswd to streamline provisioning workflows, migrate user databases, and inject initial credentials without manual terminal intervention. This guide walks through practical implementations on Ubuntu, progressing from piping individual account secrets to bulk updates from structured text files and enforcing robust cryptographic hashing schemes.
Core Mechanics and Single-Account Password Updates
To establish our baseline lab environment, provision a fresh test identity via sudo useradd -m -s /bin/bash testuser1.
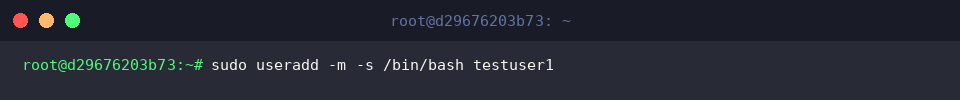
Under the hood, chpasswd ingests pairs formatted as username:password directly from stdin, circumventing the standard TTY prompt entirely. Coupling it with a shell pipe (|) allows administrators to immediately dispatch credential updates for an individual user without manual prompts.
⚙️ [Key Parameters]
-c : Explicitly declares the cipher algorithm for password hashing (such as DES, MD5, SHA256, or SHA512).-e : Signals that incoming password strings are pre-encrypted hashes rather than cleartext.-m : Enforces legacy MD5 encryption when compiling hashes.-s : Specifies custom hashing rounds for SHA-based algorithms.-R : Targets operations inside a specified chroot environment directory.
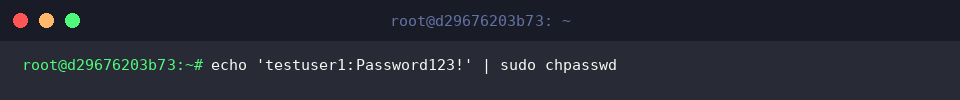
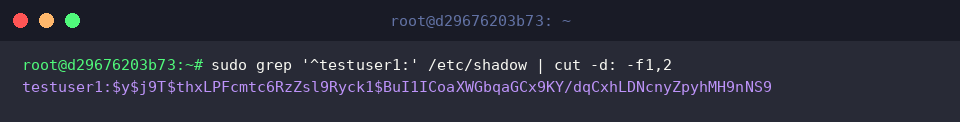
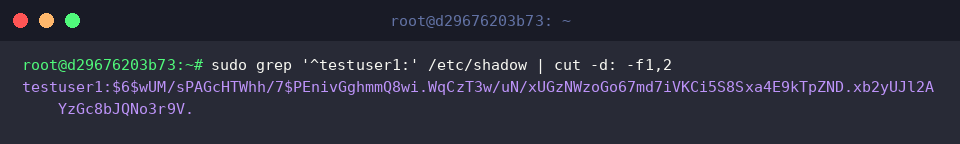
To verify that the authentication database updated as intended, inspect the cryptographic entry inside /etc/shadow. As demonstrated in the terminal output, testuser1 now features a newly minted hash securely saved to the system shadow database.
Batch Updating Multiple User Passwords Using Input Files
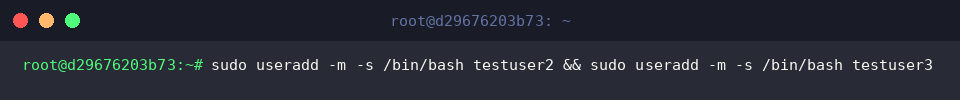
The true power of chpasswd emerges when handling bulk credentials. Let’s create two additional user accounts using sudo useradd -m -s /bin/bash testuser2 && sudo useradd -m -s /bin/bash testuser3.
Next, compile the roster of targeted accounts and their respective target passwords in username:password syntax, saving the payload into user_passwords.txt.
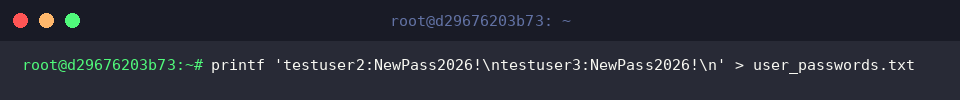
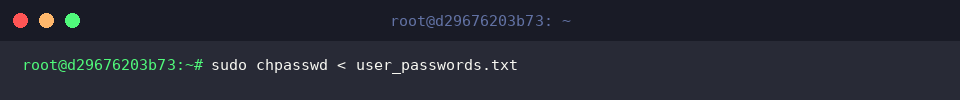
Feed this dataset into chpasswd using standard shell redirection (<). The utility processes every line sequentially in a single batch cycle, committing password revisions across multiple users simultaneously without pausing for interactive confirmation.
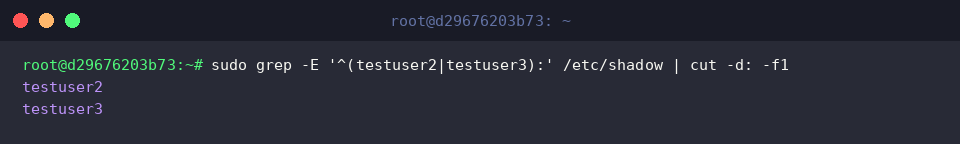
Confirm the multi-user update took effect by filtering /etc/shadow with sudo grep -E '^(testuser2|testuser3):' /etc/shadow | cut -d: -f1. The command output acknowledges valid records for both testuser2 and testuser3, confirming that the batch operation completed successfully.
Hardening Passwords with Specific Hash Ciphers (-c)
To meet organizational compliance standards or boost baseline credential entropy, pass -c SHA512 into chpasswd. This instructs PAM and the shadow suite to compute a strong SHA512 hash before writing to storage.
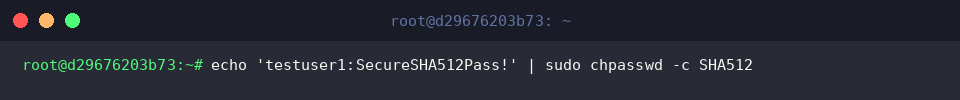
Querying /etc/shadow lets you audit whether the selected cipher was applied. The leading $6$ magic token in the second field verifies that the system transformed the secret using the SHA512 algorithm as instructed.
Post-Lab Teardown and Cleanup
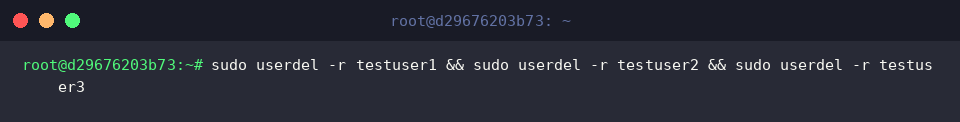
Maintaining clean lab systems prevents credential drift and lingering security exposure. Purge the temporary test accounts alongside their home filesystems by running sudo userdel -r testuser1 && sudo userdel -r testuser2 && sudo userdel -r testuser3.
Finish by stripping out any plain text password files remaining on disk via rm -f user_passwords.txt.
Mastering chpasswd equips administrators with a potent, script-friendly method for batch identity governance. Whether handling bare-metal rollouts, container initialization, or bulk credential rotations, this lightweight utility eliminates manual prompt bottlenecks while keeping user administration secure and auditable.