


Overview
Confirming that files remain uncorrupted and unaltered following network transfers or routine backups is a foundational responsibility for any Linux administrator. In this tutorial, we explore practical workflows on Ubuntu 24.04 using the built-in cksum utility to calculate cryptographic digests and validate data consistency across your filesystems.
Getting Started with cksum: Generating Single-File Checksums
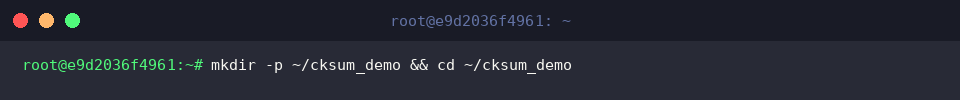
To keep our hands-on tests organized and isolated, create a dedicated workspace directory and navigate into it by running mkdir -p ~/cksum_demo && cd ~/cksum_demo.
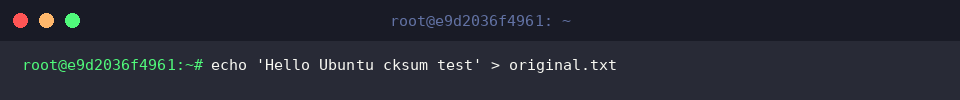
Next, generate a sample text file to serve as our baseline artifact using echo 'Hello Ubuntu cksum test' > original.txt.
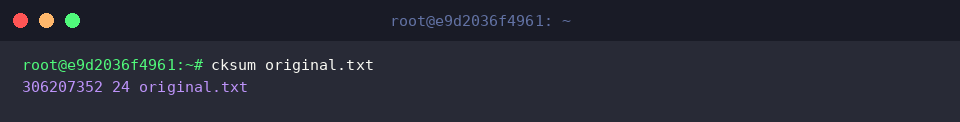
The cksum utility computes a cyclic redundancy check (CRC) along with the exact byte count of a target file to confirm that no silent data corruption has occurred.
When running standard POSIX cksum, the first field in the output represents the 32-bit CRC value, followed by the file size in bytes (24 bytes) and the target filename.
⚙️ [Essential Command-Line Options]
-a, --algorithm : Select an alternative cryptographic hashing algorithm, including md5, sha1, or sha256, rather than default POSIX CRC.-c, --check : Ingest a formatted list of recorded digests to batch-verify the integrity of referenced files.--untagged : Format the output in classic BSD/GNU reverse style without leading algorithm descriptors.--base64 : Encode resulting hash digests using base64 representation rather than standard hexadecimal strings.--raw : Produce raw binary digest bytes directly to stdout without ASCII formatting.
Multi-File Comparison and Tamper Detection
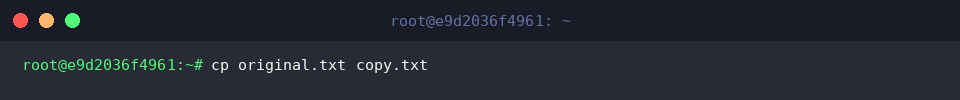
To observe how identical files evaluate, duplicate the baseline file by issuing cp original.txt copy.txt.
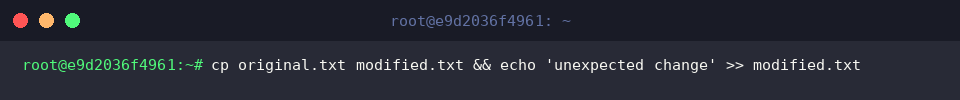
Now simulate unauthorized alteration or unexpected bit rot by cloning the source and appending an arbitrary string via cp original.txt modified.txt && echo 'unexpected change' >> modified.txt.
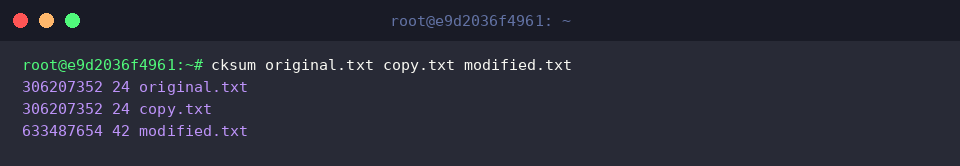
Execute cksum original.txt copy.txt modified.txt to evaluate every test candidate in a single pass.
Because original.txt and copy.txt share identical payloads, both report identical checksums (306207352) and identical lengths (24 bytes).
In stark contrast, the altered modified.txt yields a totally divergent digest (633487654) and an expanded size (42 bytes), giving system administrators an instant indicator that tampering or transmission loss has occurred.
Validating Standard Input Streams and Archived Payloads
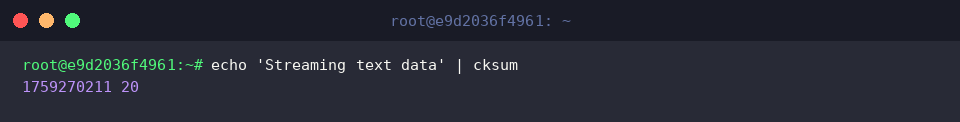
You can calculate digests for dynamic data streams directly across shell pipelines without persisting anything to disk using echo 'Streaming text data' | cksum.
The utility processes standard input seamlessly, outputting the stream’s calculated checksum (1759270211) alongside its payload length (20 bytes) on the fly.
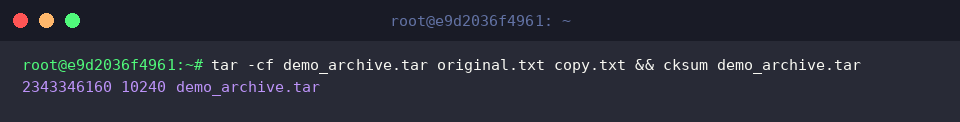
This approach also integrates smoothly with archiving routines—bundle multiple assets into a tarball and immediately derive its signature with tar -cf demo_archive.tar original.txt copy.txt && cksum demo_archive.tar.
As demonstrated in the console, demo_archive.tar returns its computed checksum (2343346160) paired with its archive size (10240 bytes) without delay.
Employing Modern Algorithms (SHA256, MD5) and Digest Files
To leverage stronger cryptographic algorithms such as SHA256, apply the -a sha256 flag and redirect the resulting hash signature into a storage file using cksum -a sha256 original.txt > original.sha256.
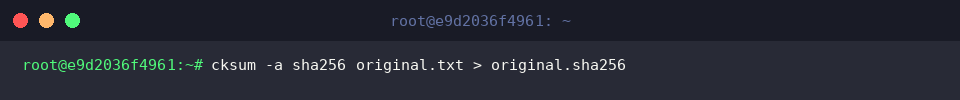
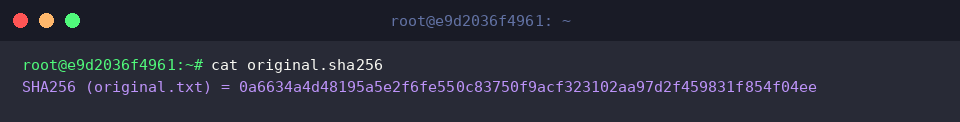
Inspect the saved manifest by running cat original.sha256.
The file contains the canonical tagged hash structure, explicitly recording the hashing method, target filename, and the complete 64-character SHA256 hexadecimal digest.
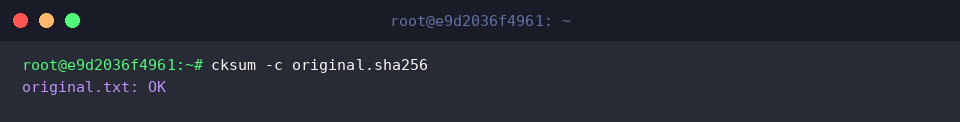
Automate file verification against your saved manifest with the -c flag by invoking cksum -c original.sha256.
The tool recomputes the hash of the referenced asset, matches it against the stored signature, and emits original.txt: OK, validating that the file has remained perfectly intact.
You now have a solid understanding of leveraging cksum on Ubuntu systems to safeguard data integrity and audit checksums efficiently.
Incorporate these diagnostic workflows into your deployment pipelines and backup routines whenever you need rapid, dependable verification against tampering or bitrot.